- contact@insightfortify.com
InsightFortify · AI-native application security posture
Thousands of scanner alerts. The few that can actually hurt you.
InsightFortify runs the scanners you trust across code, dependencies, secrets, infrastructure, web apps, APIs, AI models and cloud accounts. It merges what they report into one queue and scores each finding by whether it can be exploited here: known exploitation, internet exposure, sensitive data and runtime evidence. Developers get the fix, not the CVE number.
- 66% fewer findings to act on
- Runs in your cloud
- Every score explains itself
Built on the open-source scanners security teams already trust
TrivyOpengrepGitleaksSyft
CheckovOWASP ZAPProwlerFalco
CISA KEVFIRST EPSSOSV
The problem
Security teams don’t lack findings. They lack a reason to fix one before another.
Every scanner is right about what it sees and wrong about what matters. The same vulnerable library shows up in five tools, a critical CVE sits in a test fixture, and the exposed admin key in last year’s commit is at the bottom of a list of 4,000. Developers stop reading. The board asks whether you are getting safer, and nobody can answer.
Noise
The same issue, five times
SCA, container and SBOM tools each report the same package. Duplicate tickets erode developers’ trust faster than any false positive.
No context
“Critical” says nothing about your environment
CVSS rates the bug, not the deployment. A critical in a dev-only dependency matters less than a medium on an internet-facing service that holds card data.
New surface
AI code and agents arrived faster than policy
Assistants write a growing share of code, teams ship LLM features and agents with tool access, and none of it fits the old scanner categories.
Measured, not promised
From raw output to the list worth fixing
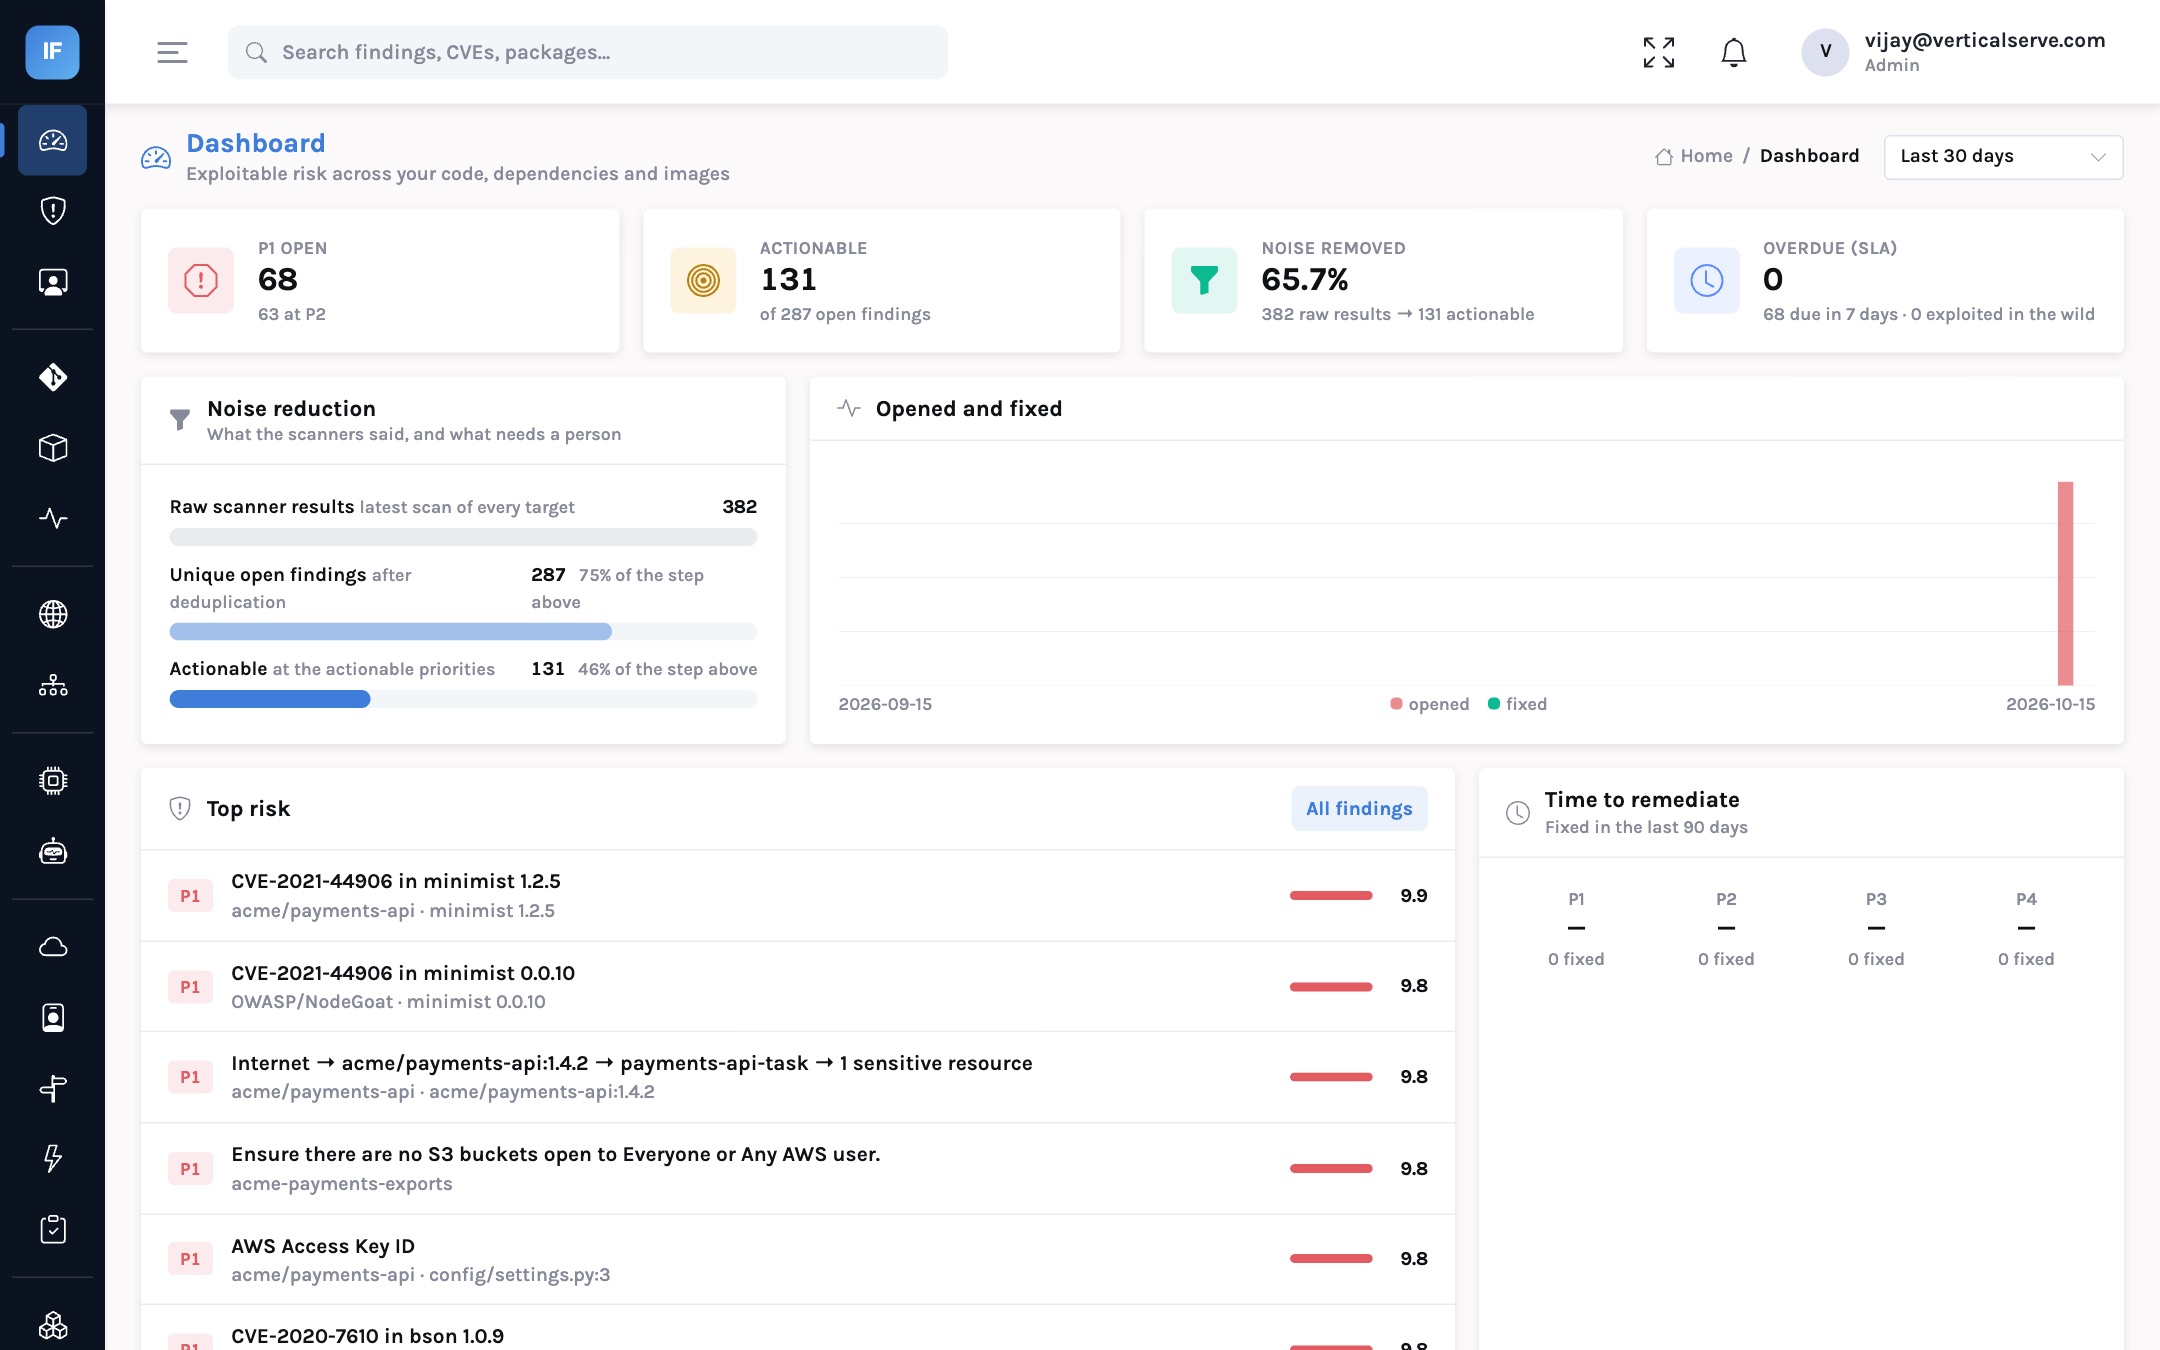
These numbers come from our own demo estate: two sample services, OWASP NodeGoat, a local OWASP Juice Shop under a ZAP scan, and one AWS account. Correlation removes duplicates; context removes what cannot be reached. What remains is what we would ask a developer to fix this sprint.
On NodeGoat alone, 340 raw results became 215 unique findings and then 80 actionable ones.
Raw scanner results382
Unique, after correlation287
Actionable, after context131
66% fewer items to act on. Nothing is deleted: every suppressed or deprioritised finding stays in the queue with the reason recorded.
How it works
Scan → Correlate → Prioritise → Fix
One pipeline for every kind of finding. You don’t replace your scanners or your workflow; you add the layer that decides what to do first.
1
Scan
Repositories on push or schedule, CI pipelines through one API call, web apps and APIs a security lead has verified as yours, cloud accounts through a read-only role. Or upload results from scanners you already run.
2
Correlate
Every result is normalised and fingerprinted, so the same issue from five tools, across branches and rescans, is one finding with five sources attached.
3
Prioritise
A 0–10 score built from named factors: CVSS, CISA KEV, EPSS, internet exposure, sensitive data, runtime evidence, test code and dev-only scope. P1–P4 with an SLA for each.
4
Fix
The fixed version, the code change or the policy to apply, an AI explanation in plain language, and a CI gate that blocks only what you decide should block.
A score that shows its work
Why this finding is P1, line by line
No black box. Each priority comes with the factors that produced it, so a developer can disagree with a specific line instead of the whole tool.
- CVSS 7.5the published base score7.5
- Exploited in the wildlisted in the CISA KEV catalog+2.0
- Internet-facingthe service is reachable from the internet+1.0
- Handles sensitive datapayment card data, PII+0.5
- Compensating controlsWAF in front of the service−0.5
- Score → P1, fix within 7 days9.6
In the pipeline
One call from any CI system
The pipeline posts its scan results and gets back a pass or fail decision based on your gate policy: new P1s only, no new secrets, nothing on KEV.
# any CI system: scan, then ask for a decision
trivy fs --format json --list-all-pkgs -o trivy.json .
gitleaks detect --report-format json --report-path leaks.json --exit-code 0
jq -n --slurpfile t trivy.json --slurpfile g leaks.json \
  '{repository: env.GITHUB_REPOSITORY, commit: env.GITHUB_SHA,
    outputs: {trivy: $t[0], gitleaks: $g[0]}}' |
curl -sf -H "Authorization: Bearer $FORTIFY_API_KEY" \
  -H 'content-type: application/json' -d @- $FORTIFY_URL/api/ci/scan |
jq -e '.data.gate.result == "pass"'
# fail → "blocking": [{"title": "…", "priority": "P1", "file": "…"}]
Coverage
Code to cloud, in one queue
Each surface uses a proven open-source engine, so you can check our findings against the tool itself. InsightFortify adds correlation, context, prioritisation and the fix.
Code
Source & secrets
Static analysis with Opengrep; secrets with Gitleaks across the full git history, not just the latest commit.
- Rotation tracked as a triage action
- Test code and fixtures recognised
- Your own secret patterns, in CI too
Supply chain
Dependencies & SBOM
Trivy for open-source packages and container images; Syft for CycloneDX SBOMs, with each component searchable across the estate.
- “Where do we run log4j?” in one search
- Dev-only and transitive scope
- KEV and EPSS on every CVE
Infrastructure
IaC
Checkov on Terraform, CloudFormation, Kubernetes and Dockerfiles, so a public bucket is caught at the pull request, before it is deployed.
- Benchmark mappings kept for compliance
- Same queue, same SLA
Applications
Web apps & APIs
OWASP ZAP dynamic testing against targets a security lead has verified, plus an API inventory built from code, specifications and observed traffic.
- Verified, audited targets only
- Shadow (undocumented) API detection
- Runtime evidence raises the score
AI
AI apps & agents
Inventory of models, prompts and agents in code; prompt-injection and data-leak findings; runtime guardrails and tool-permission policies for agents.
- OWASP LLM Top 10 mapping
- Agent tool-call audit trail
Cloud
Cloud, identities & runtime
Prowler posture checks, IAM entitlements with blast radius, attack paths from the internet to sensitive data, and Falco runtime detections.
- CIS, NIST, PCI, SOC 2 failure view
- Least-privilege policy suggestions
Attack paths
Findings that look manageable alone can add up to one critical path
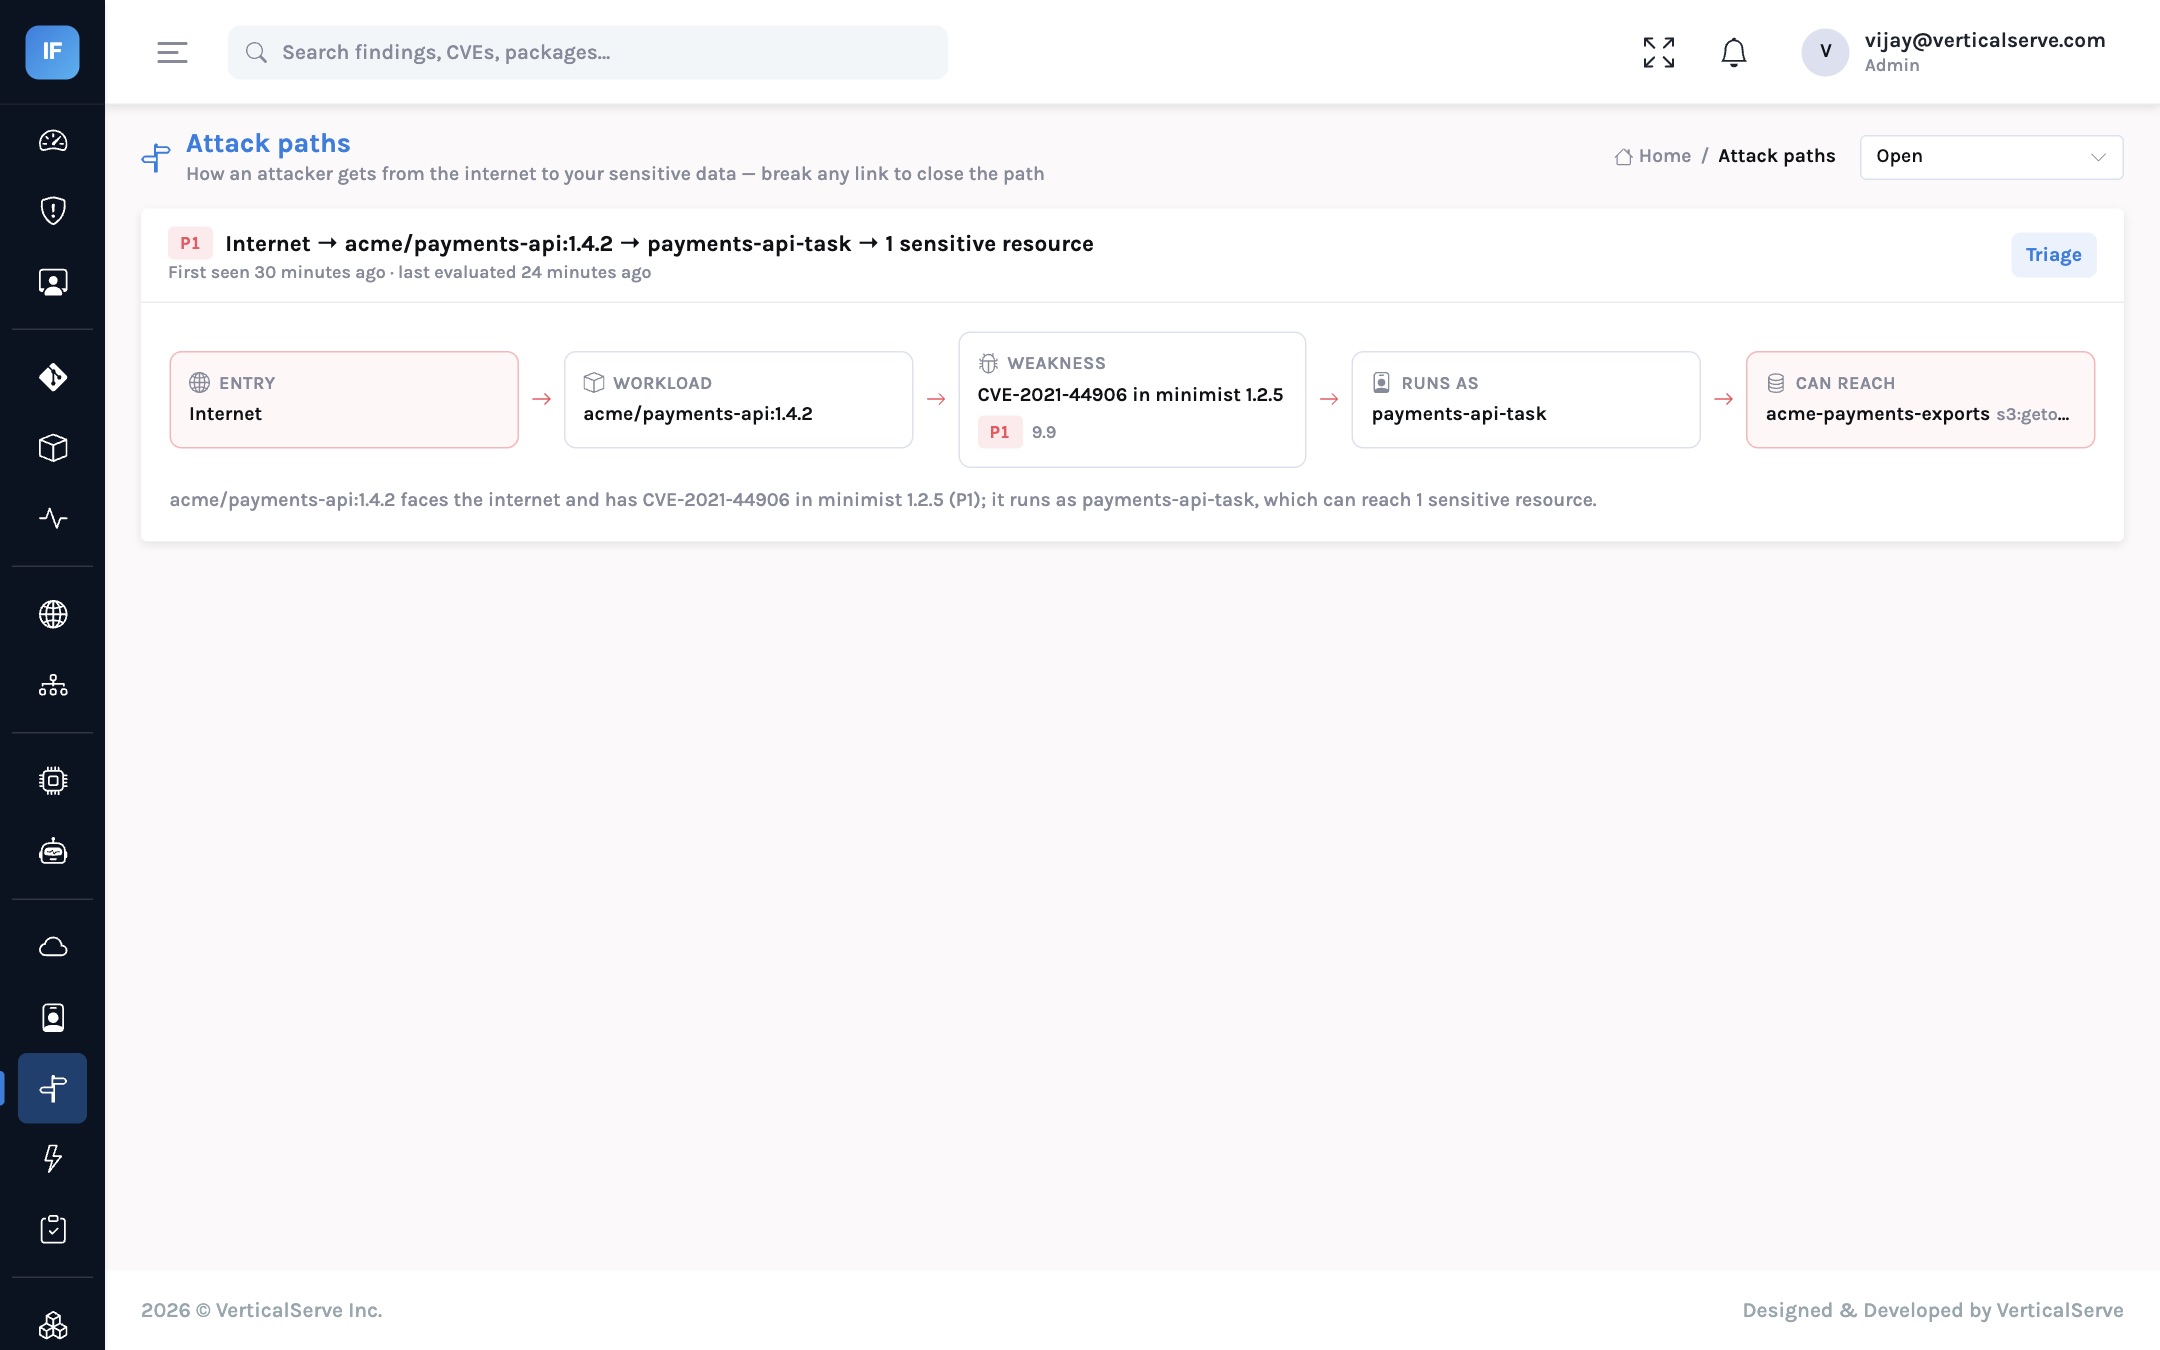
On their own, none of these would top a list. Joined together they are a straight line from the internet to payment data, and InsightFortify ranks the path, not the parts. This is the path in our demo account.
ExposureInterneta public load balancer in front of the service
Workloadpayments-apiits image carries a critical, fixable CVE
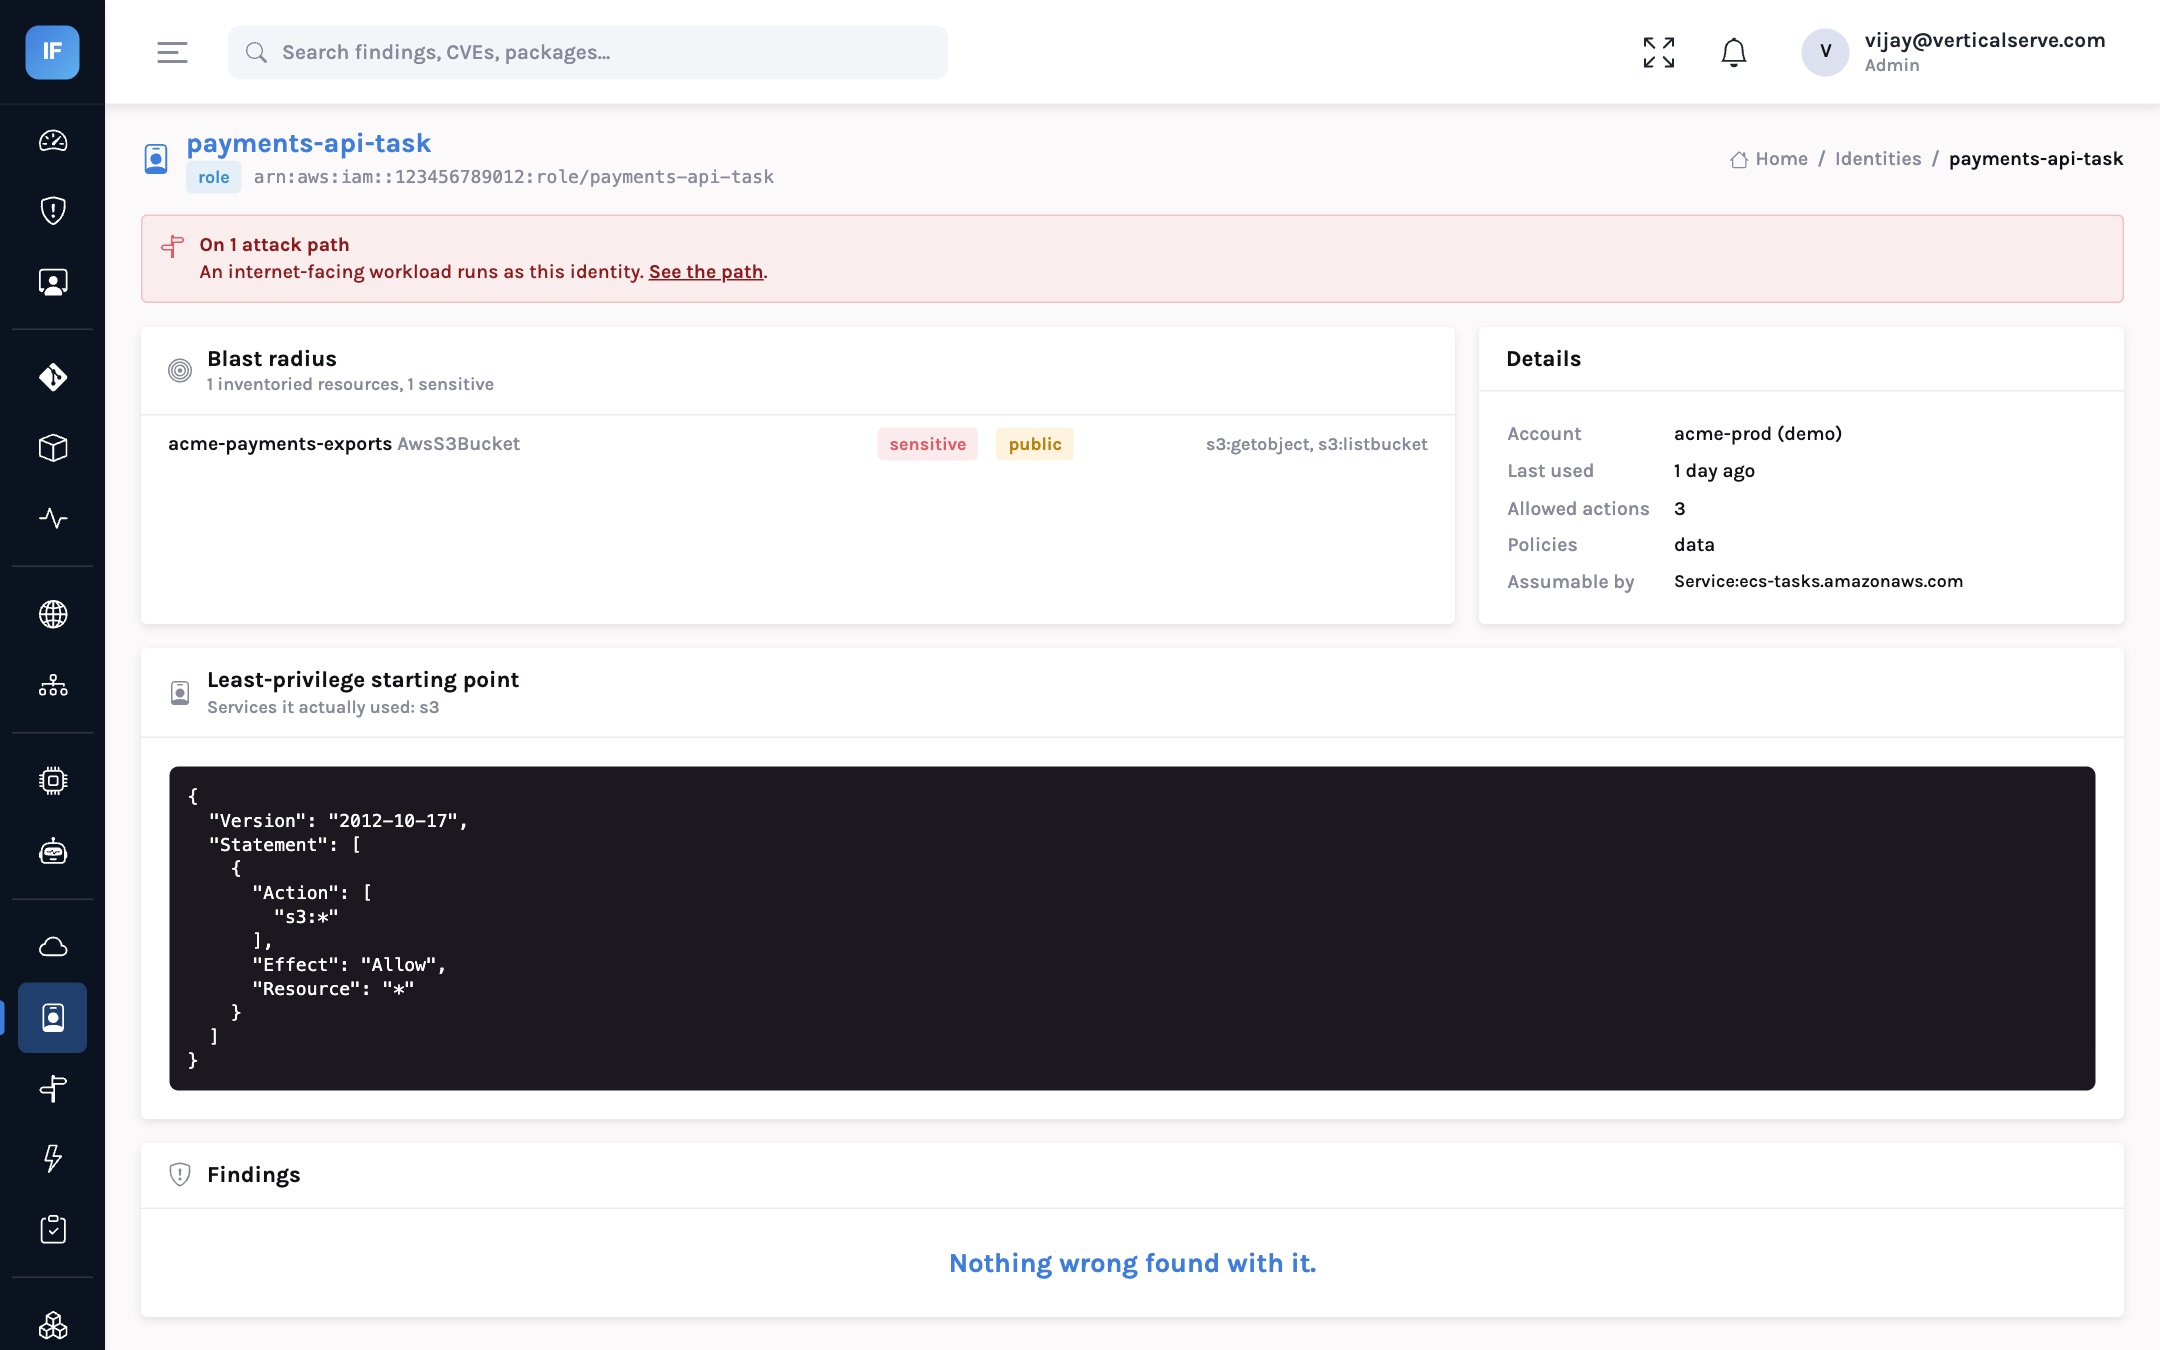
Identitypayments-api-taskthe role the task runs as can read the exports bucket
Dataacme-payments-exportsmarked sensitive
The console
One queue for AppSec, one answer for the board
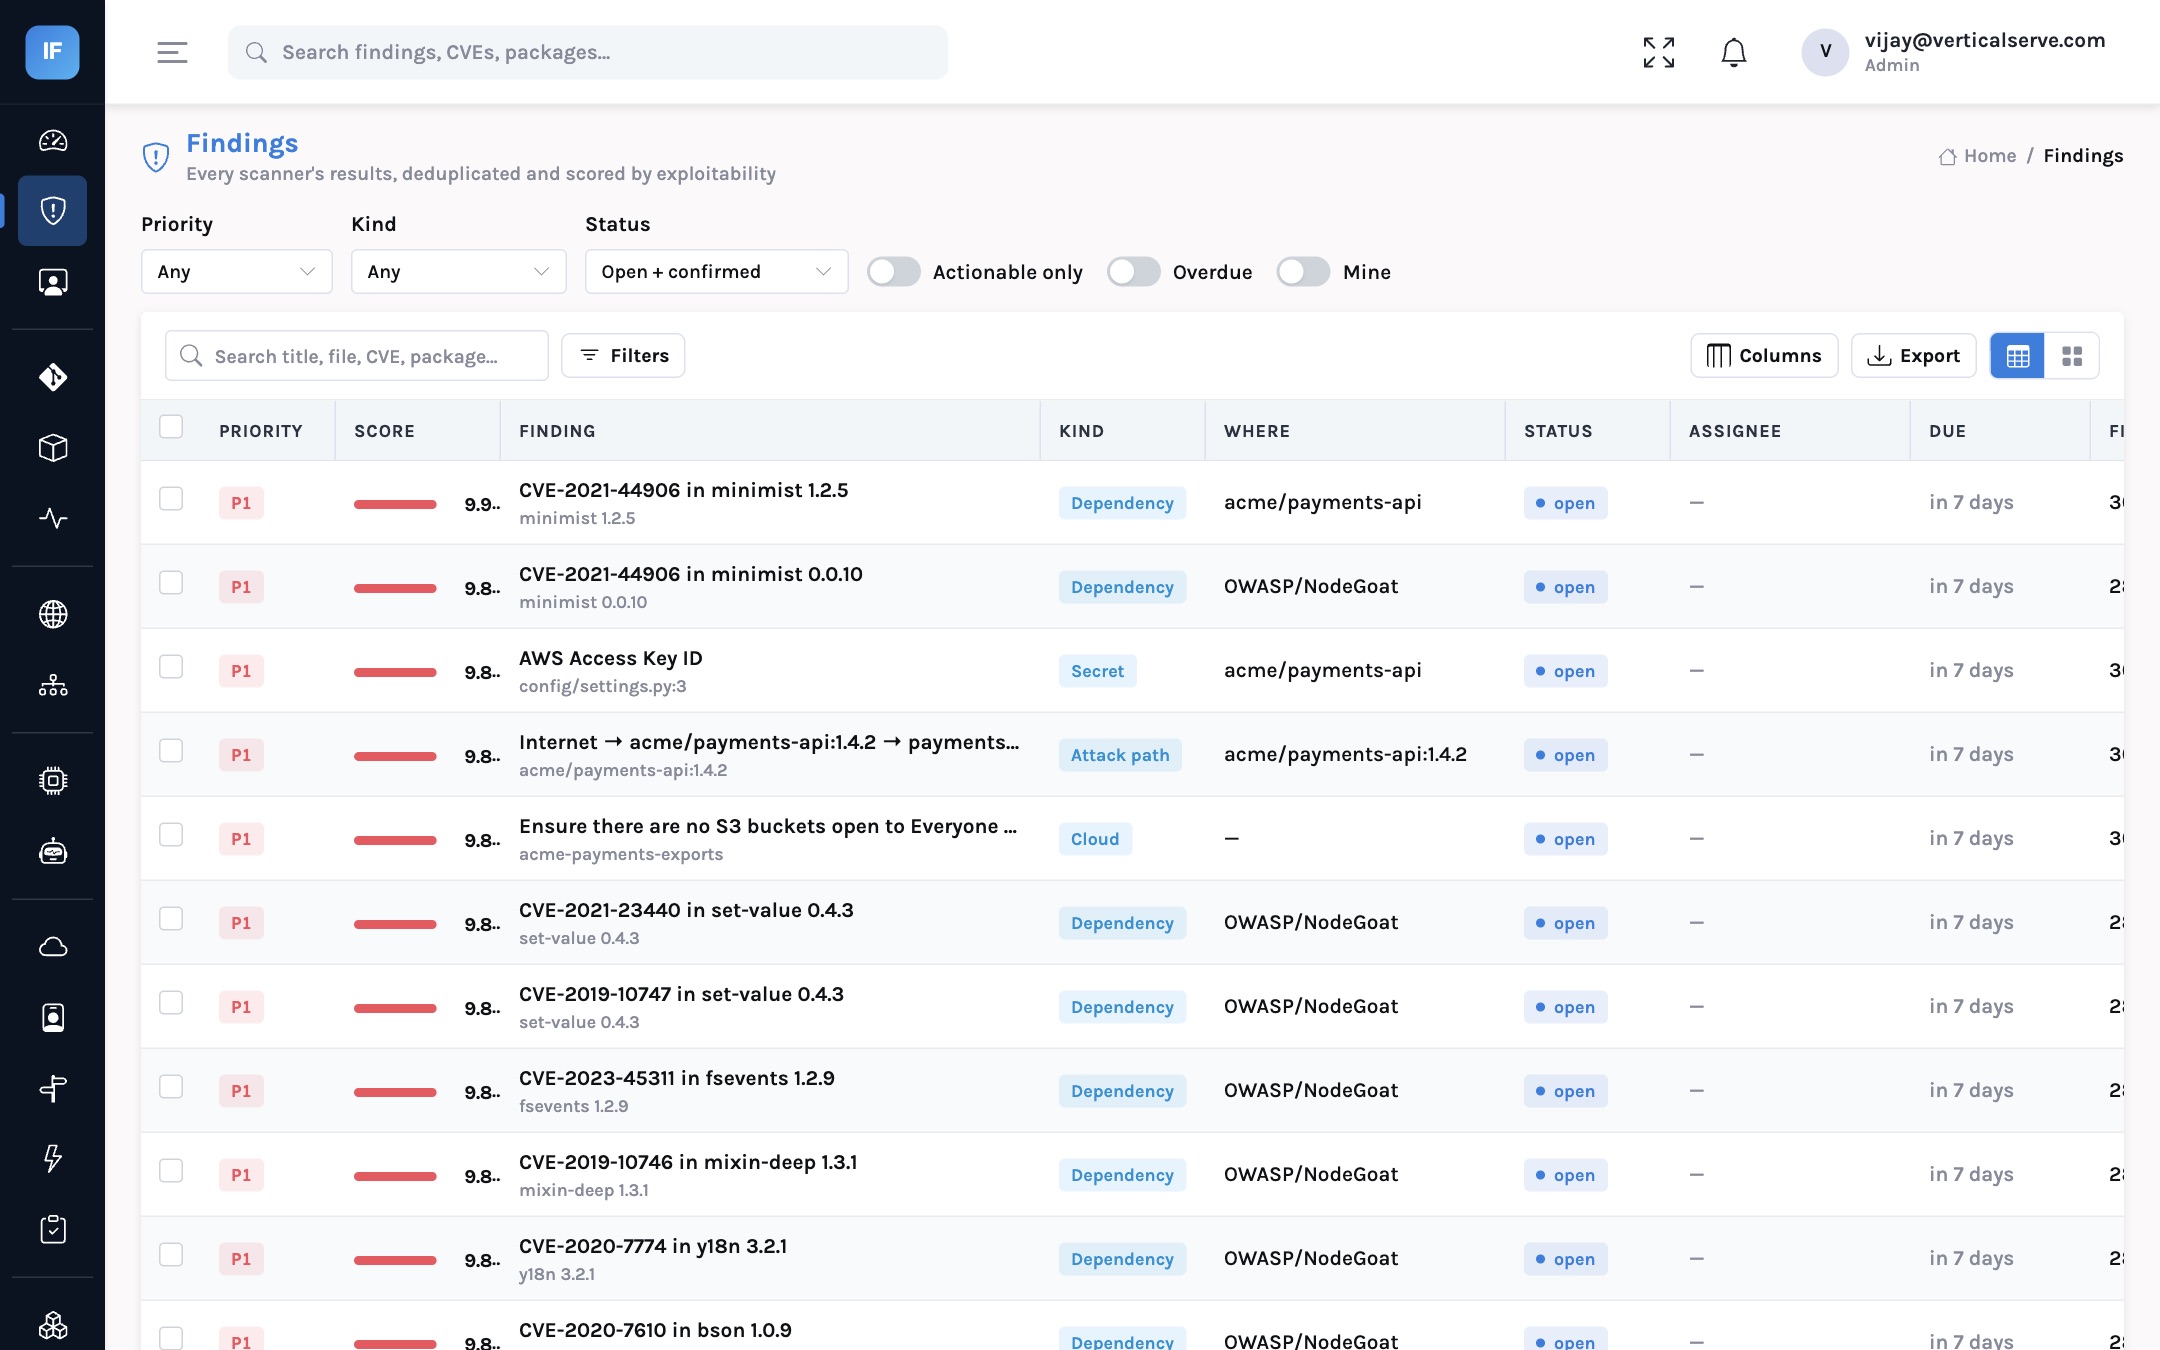
Analysts triage with the evidence and the score breakdown. Developers see only their services and the fix. Leadership sees the trend, the SLA position and the compliance gaps.
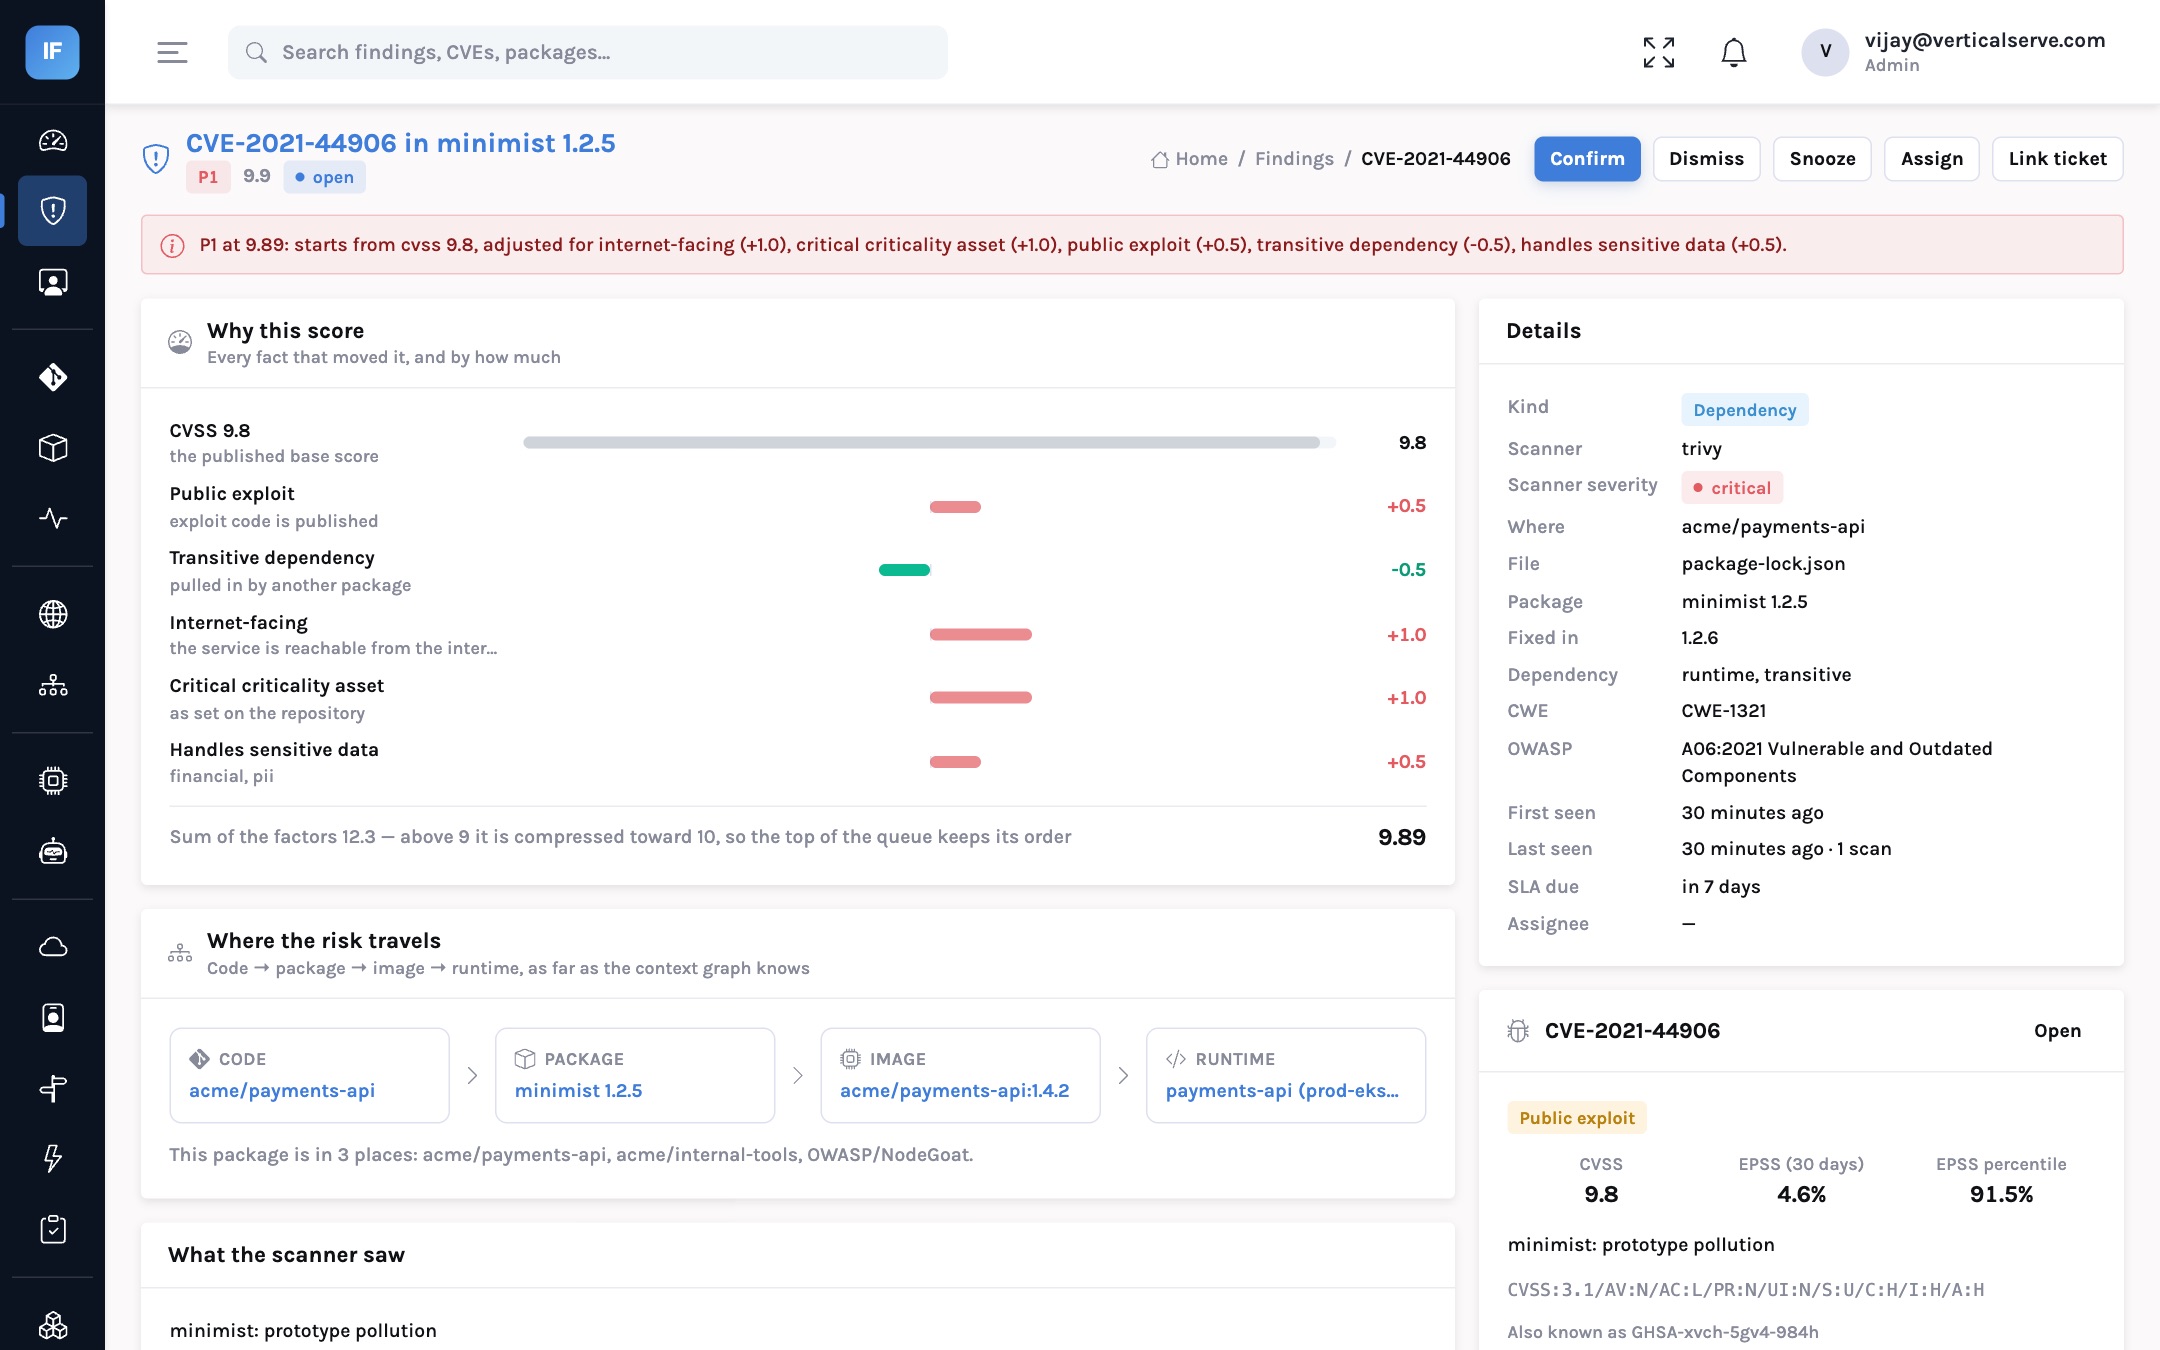
For security leaders
Numbers you can take to the board
The questions a CISO is asked are simple. The data to answer them is usually scattered across eight tools. InsightFortify keeps it in one place.
Are we getting safer?
Open P1/P2 trend, new versus fixed, and mean time to remediate by priority and by team.
Are we meeting SLA?
Per-priority SLAs you set, breaches surfaced before an auditor finds them, and every dismissal or snooze recorded with who and why.
Where do we fail audit?
Requirements failed by open findings, by framework: CIS, NIST 800-53, PCI DSS, SOC 2, ISO 27001.
What is our AI exposure?
Every model, prompt and agent in the estate, what each can touch, and what guardrails stopped.
Deployment & trust
Your code never leaves your cloud
InsightFortify is a modular monolith on PostgreSQL and Redis. Scanners run as workers next to your code. It is a single product to deploy in your account, not another SaaS that needs read access to every repository.
Isolation
Tenant isolation in the database
PostgreSQL row-level security on every tenant table, so a missed filter in application code still returns nothing from another organisation.
Secrets
Credentials by reference
Cloud roles and tokens are stored as references to your secret manager, never as values. Cloud access is read-only and assumed per scan.
Safety
Scans only what you own
A dynamic scan is an attack. It runs only after a security lead verifies the target is yours to test, and their written attestation is kept in the audit trail.